Loading...
personal
My Data Manager: Zero-Trust Encryption with Node.js Crypto
Node.jsExpress.jsMongoDBCrypto (AES-256-GCMPBKDF2)
Overview
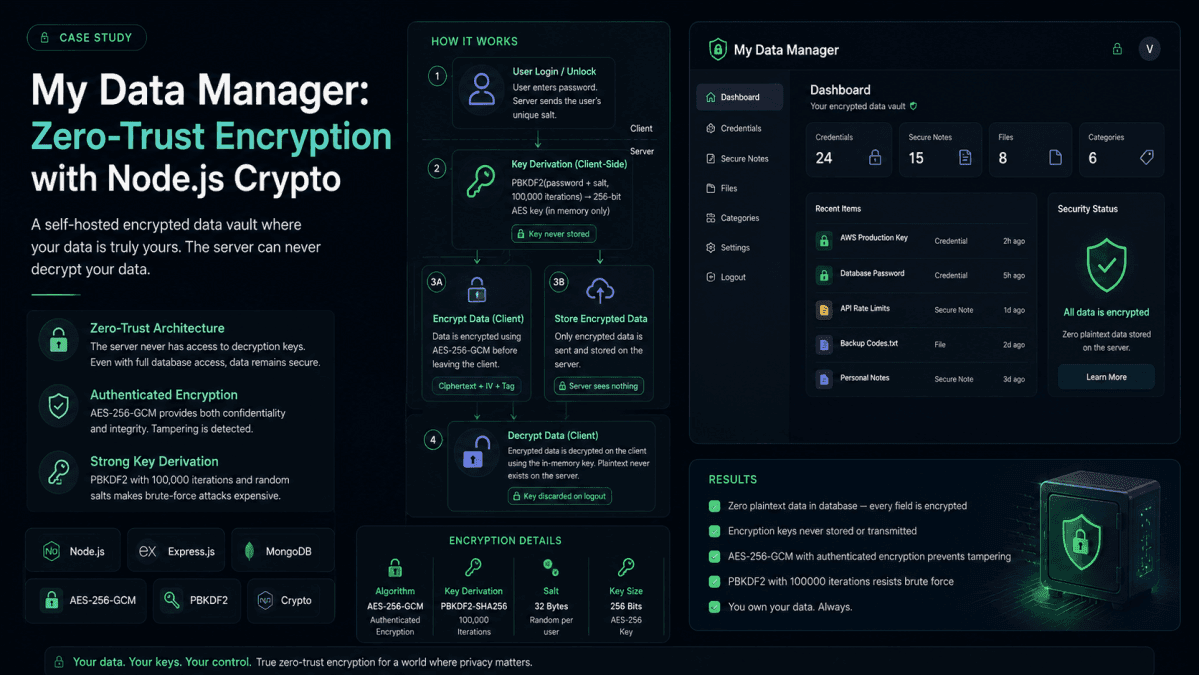
My Data Manager is a self-hosted encrypted data vault built on a zero-trust architecture — the server can never decrypt user data, even with full database access. The platform uses AES-256-GCM authenticated encryption with PBKDF2 key derivation.
Problem
Most encrypted apps use encryption-at-rest where the server holds the decryption key. This means anyone with server access, a court order, or a successful exploit can read user data. For sensitive information like credentials and API keys, this model is unacceptable.
Solution
Built a system where encryption keys are derived at runtime from the user's password using PBKDF2 with 100,000 iterations and a random 32-byte salt. The derived key is never stored — it exists only in memory for the session duration and is discarded on logout.
Technical Architecture
- Backend: Node.js, Express.js
- Encryption: AES-256-GCM via Node.js native crypto module
- Key Derivation: PBKDF2 with per-user random salts
- Storage: MongoDB with encrypted fields only
- Client: Minimal frontend for credential and file management
Results
- Zero plaintext data in database — every field is encrypted
- Encryption keys never stored or transmitted
- AES-256-GCM with authenticated encryption prevents tampering
- PBKDF2 with 100000 iterations resists brute force
Was this case study helpful?
Comments
0Be the first to share your thoughts.